
What Is Data Sovereignty?
Data sovereignty is the principle that data generated or collected within a specific country is subject to the laws of that country. This principle applies to almost all data types, including personal information, financial records, or intellectual property.
Data sovereignty is vital to national security because responsible governments regulate the storage and processing of sensitive data. This should prevent security breaches and unauthorized usage of said data by foreign or unregulated entities.
For the individual, “awareness” of their data privacy laws increased confidence levels for maintaining their own data privacy by over 35% compared to those who were unaware, according to a study by Cisco.
Ownership vs. Privacy vs. Localization vs. Residency vs. Sovereignty
The semantics surrounding data, the lawful handling of it, and who has the right to it has driven the development of many phrases.
You generate data, of which you are the creator, but not necessarily the owner (Data Ownership).
That data is subject to privacy laws (Data Privacy), which may define that your data stays within a specific region or geographic boundary (Data Localization).
The data you created might reside in a different country (Data Residency), which may have additive rules and restrictions based on their own laws and authority of applicable jurisdictions (Data Sovereignty).
Data Ownership identifies the individual or organization with recognized authority and responsibility for a data asset, including decisions about its access and use. In governance contexts, ownership does not necessarily mean absolute legal property rights and is often expressed through accountability and control over data. (DAMA)
DAMA® Data Management Body of Knowledge (DAMA-DMBOK®)
Data Privacy concerns the appropriate collection, processing, use, disclosure, retention, and protection of personal information. It focuses on individuals' rights and organizations' responsibilities regarding personal data rather than primarily on where that data is stored. (NIST)
Data Localization refers to legal or regulatory requirements that data be stored, processed, or otherwise handled within a specified geographic jurisdiction. Unlike broader data-sovereignty concerns, localization specifically imposes geographic constraints on where data can reside or be processed. (Congress)
Data Residency describes the physical or geographic location where an organization's data is stored or processed. It identifies where data resides, while sovereignty addresses the laws and jurisdiction governing that data. (IBM)
Data Sovereignty is the principle that data is subject to the laws and governance requirements of the jurisdiction in which it is stored or processed. It focuses on which government or legal authority has jurisdiction over the data. (IBM)
How Does Sovereignty Impact Data Privacy and Security?
Sovereignty is intrinsically linked to data privacy, which ensures data is governed by the jurisdictional rules of the nation in which it resides and where its users are citizens. Organizations must adhere to these local data privacy laws, which often include restrictions for:
- Data collection
- Data processing
- Data sharing
- Data storage
- Data access
- Data governance
Additionally, privacy laws typically emphasize data protection, mandating robust security measures like encryption, access control, continuous monitoring, and more. That means foreign organizations are subject to local regulation if they handle data that originates within their legal jurisdiction.
Notable Frameworks
A challenge that companies frequently face is the numerous frameworks that require navigation. Below is a table of the most common data regulations we’ve seen.
| Name of Framework | Name of Country | Year Put Into Law | Country Documentation | How to Be Compliant? |
|---|---|---|---|---|
| GDPR – General Data Protection Regulation | European Union | 2016; applied 2018 | European Commission – Data Protection | GDPR Compliance |
| CCPA / CPRA | United States – California | CCPA 2018; CPRA 2020 | California Privacy Protection Agency | CCPA Compliance |
| PIPL – Personal Information Protection Law | China | 2021 | Government of China | |
| Data Security Law (DSL) | China | 2021 | Government of China | |
| DPDPA – Digital Personal Data Protection Act | India | 2023 | Ministry of Electronics & IT | DPDPA Compliance |
| LGPD – Lei Geral de Proteção de Dados | Brazil | 2018 | ANPD | |
| APPI – Act on the Protection of Personal Information | Japan | 2003 | Personal Information Protection Commission | |
| PDPA – Personal Data Protection Act | Singapore | 2012 | Personal Data Protection Commission | |
| PIPA – Personal Information Protection Act | South Korea | 2011 | Personal Information Protection Commission | PIPA Compliance |
| EU Data Act | European Union | 2023; applied 2025 | European Commission – Data Act | EU Compliance |
| CLOUD Act | United States | 2018 | U.S. Department of Justice – CLOUD Act |
Data Sovereignty Compliance Best Practices
Conduct a data audit
Knowing where your data is collected, stored, processed, and transmitted is essential to maintaining compliance. Conduct an audit and map cross-border data flows to identify your relevant jurisdictions.
Understand your compliance landscape
Thoroughly research and comprehend the exact data privacy laws in each country where you operate. This includes understanding specific requirements for data collection, storage, and processing.
Consulting with legal experts or hiring a compliance officer with expertise in international data protection laws can help navigate these complexities. This foundational knowledge is crucial for developing effective data management strategies that align with local legal frameworks.
Use local data centers
Local data centers help you comply with localization requirements, which ensures information remains within reach of the local authorities.
For multinational companies, this might involve setting up multiple data centers in different regions, which can be coordinated through a hybrid cloud approach to balance local compliance with operational efficiency.
Implement data governance policies
Internal policies should outline procedures for data management, including data classification, access controls, data handling protocols, and compliance monitoring.
Establish an oversight framework that assigns clear responsibilities for data protection and compliance. Regularly review and update these policies to adapt to changing regulations and business needs, ensuring all aspects are compliant and secure.
Leverage the right solutions
A robust identity and access management (IAM) platform can offer several control mechanisms, such as multi-factor authentication (MFA) and risk-based adaptive authentication, to restrict data access to authorized personnel only.
Get Visibility and Control of Your Cryptographic Assets for Data Sovereignty with CSP
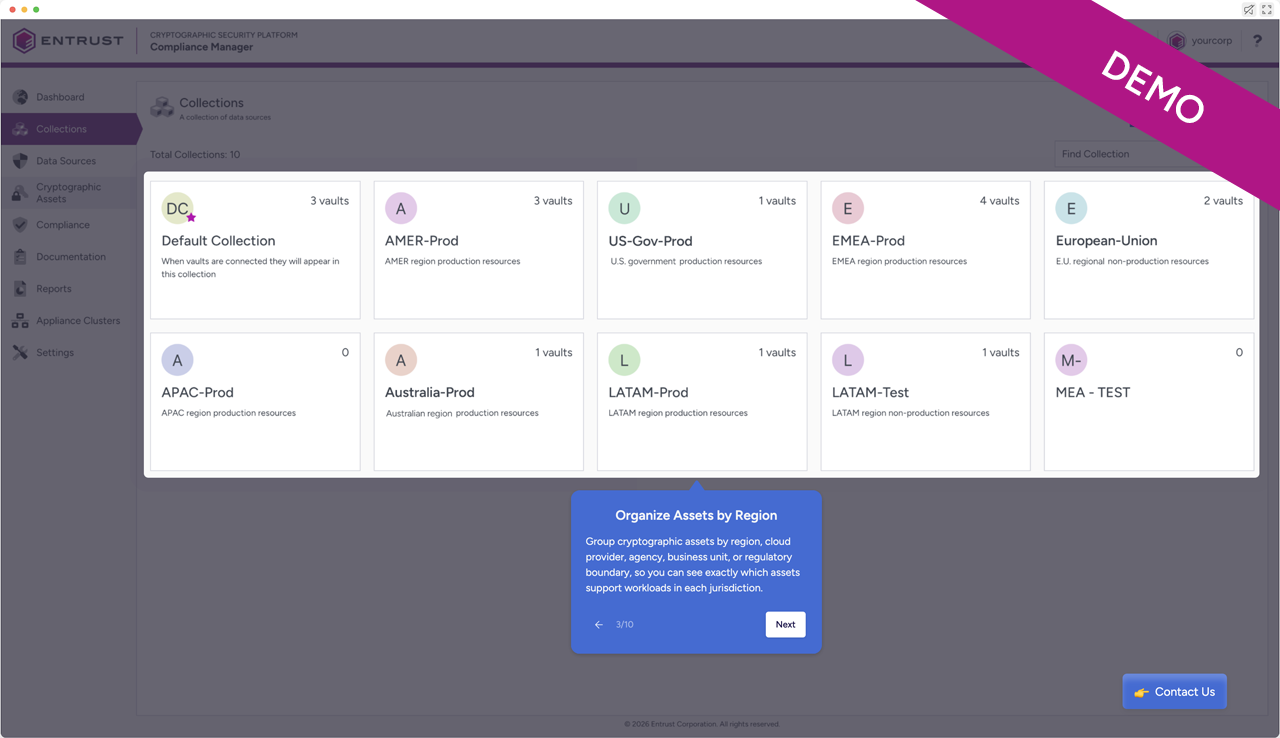
Data is global, but regulations are local. Knowing where your encryption keys are, who controls them, and their compliance status is essential to maintain data sovereignty and meet the requirements of regional regulations, such as FedRAMP, GDPR, CJIS, and NIS2.
The Entrust Cryptographic Security Platform enables you to discover, own, and govern cryptographic assets wherever your data lives.
Explore our demo to see how.
Data Sovereignty Solutions
Entrust nShield HSMs
Create, use, and protect cryptographic keys in hardened, FIPS-certified hardware security module for a secure root of trust.
Entrust Cryptographic Security Platform
Get complete visibility and control over your cryptographic estate – PKI, HSMs, and key, certificate, and secrets lifecycle management – in a single platform designed for crypto-agility and resilience.
Entrust Cryptographic Security Platform Key Manager
Our cryptographic key lifecycle management solution provides centralized visibility and auditing across the organization, along with decentralized vaults, to help enable compliance with data sovereignty regulations.
Explore Compliance Management Solutions
From encryption and authentication to hardware security modules (HSMs) and public key infrastructure (PKI), learn how Entrust solutions can help you meet your many compliance requirements.
Legislative and regulatory requirements can vary by jurisdiction, industry, product, and use case and may change over time. The information provided on this page is for general informational purposes only and reflects our understanding as of the date of publication. It does not constitute, and should not be relied upon as, legal, regulatory, or compliance advice. You should consult your own legal, compliance, or regulatory advisors regarding any questions or requirements that may apply to your business.